Client-Side Encryption vs Server-Side Encryption
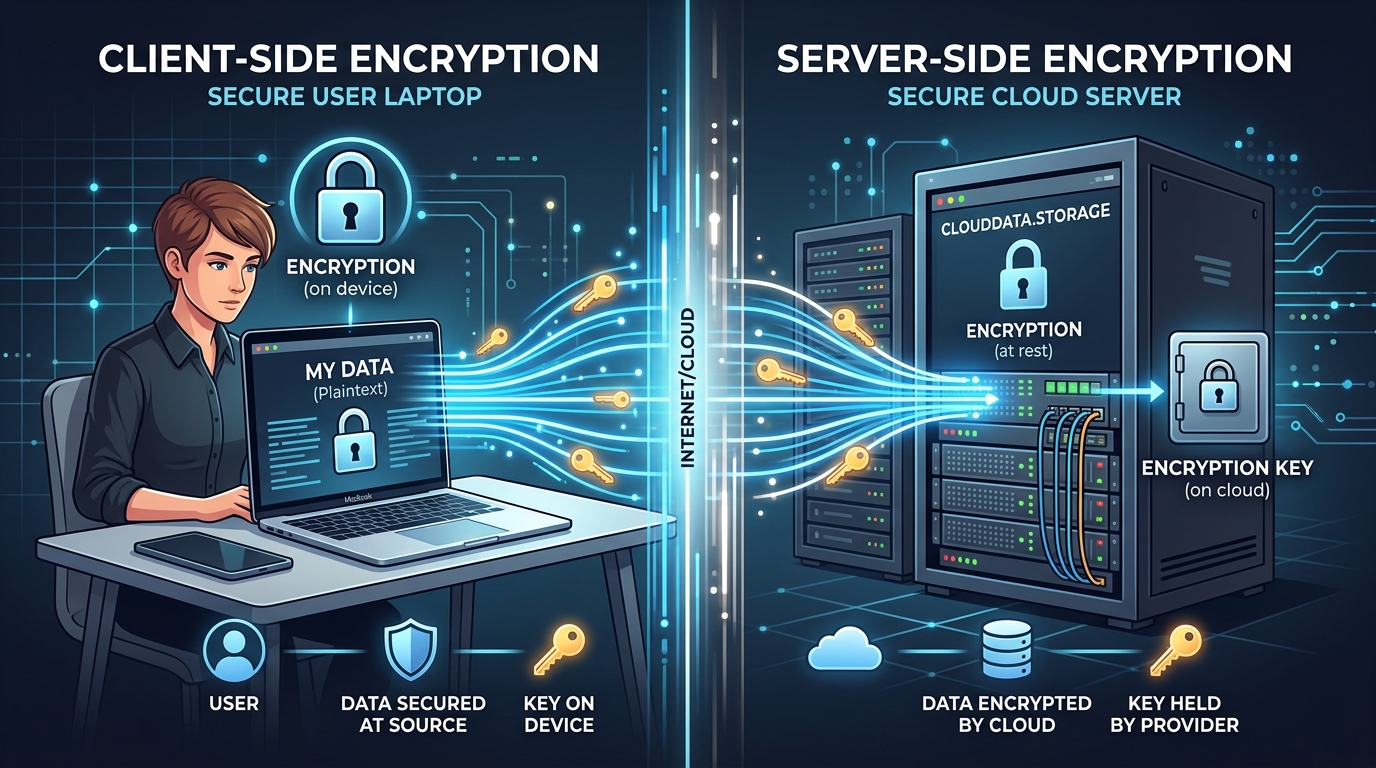
Client-Side Encryption vs Server-Side Encryption
When evaluating cloud storage platforms, encryption is the primary shield guarding your data. However, not all encryption is deployed in the same way. The two most common methodologies are Client-Side Encryption (CSE) and Server-Side Encryption (SSE). Understanding the difference is crucial for establishing your organization's data security posture.
Server-Side Encryption (SSE)
Server-Side Encryption is the industry standard for most major cloud providers. In this model, data is encrypted after it reaches the cloud provider's servers.
How it works:
- You upload a file over a secure connection (TLS/SSL).
- Once the server receives the file, the provider's system generates an encryption key.
- The provider encrypts the file and stores it on their hard drives.
- The provider securely manages and rotates the encryption keys.
Pros and Cons: SSE is highly convenient. Because the provider manages the keys, they can offer features like password resets, web-based file previews, and seamless third-party app integrations. However, because the provider holds the keys, you must trust their internal security practices to protect your data from insider threats or breaches.
Client-Side Encryption (CSE)
Client-Side Encryption flips the model by encrypting the data before it leaves your device.
How it works:
- The encryption software on your device generates a key.
- The file is encrypted locally on your computer or phone.
- Only the encrypted ciphertext is sent to the cloud provider.
- The cloud provider never sees the file in its raw form and never has access to the key.
Pros and Cons: CSE provides a higher level of privacy since the cloud provider is completely blind to the data payload. However, it places the burden of key management entirely on the user. If the user loses their key or password, the data cannot be recovered by the provider.
The QuixiCloud Advantage
Choosing between usability and security is a common dilemma. QuixiCloud bridges this gap through a strict privacy-first architecture.
We provide advanced AES-256 encryption to ensure your data is mathematically secure against brute-force attacks. Furthermore, QuixiCloud offers powerful client-side tools designed to give you granular control over your data workflows. Our infrastructure ensures that whether your data is in transit or at rest, it is shielded by enterprise-grade cryptographic standards, giving you peace of mind without sacrificing performance.
Next Steps in Data Privacy
True data security requires a robust infrastructure. Explore QuixiCloud Secure Cloud Storage to see how our strict privacy-first architecture and advanced AES-256 encryption keep your sensitive information completely safe.
Explore More: Best Encrypted Cloud Storage · Best Secure Cloud Storage · Secure Cloud Storage Solution
Written by QuixiCloud Security Team
The QuixiCloud Engineering Team is dedicated to building secure, scalable, and privacy-first cloud storage solutions.